Browser Extension Security for Teams in 2026: A Simple Audit Guide
A browser extension can save time by filling forms, checking grammar, managing passwords, or helping with meetings. It may also read pages, change what a user sees, or send data to an outside service. That makes extensions a useful part of work and a real security concern. Small teams often install them one at a time, then forget which ones still have access.
This guide explains how to audit browser extensions on company devices, check permissions, and create a simple approval process. The goal is not to ban every helpful tool. It is to know what is installed, what it can reach, and how to remove access that no longer serves a task.
Begin With an Extension Inventory
Ask staff to list extensions used for work and the browser profile where each runs. Include the extension name, publisher, purpose, install date if known, permissions, and the person who needs it. A tool used by one employee should not silently become standard across the whole company.
Look for duplicates that solve the same job. A team may have three screenshot tools when one approved tool would do. Remove extensions no longer used. Fewer add-ons make the browser easier to maintain and reduce the number of services that may see page content.
Use a separate work profile
A work browser profile can help separate company accounts and extensions from personal browsing. It does not replace device security, but it makes the approved list easier to manage. Tell staff which profile to use for work and how to request a new extension. Avoid asking people to install work add-ons in private profiles.
Understand Permissions Before Installing
An extension may ask to read data on the websites you visit, change page content, manage downloads, or access clipboard data. Some permissions make sense for a specific task. Others may be too broad. Check whether the extension needs access to all sites or only a few approved domains. Prefer a narrow grant when the browser supports it.
Chrome’s permission warning guidance explains why browsers show warnings when extensions request certain capabilities. A warning is a prompt to review, not proof that the extension is harmful. The right question is whether the requested access matches the job.
Think about sensitive sites
A tool that reads every page may see internal dashboards, support records, webmail, or financial data. Ask if it needs those pages. If not, restrict site access or choose another extension. Do not assume a helpful product name makes broad access safe. Treat browser add-ons as software with permissions, not as small cosmetic features.
Check the Publisher and Update History
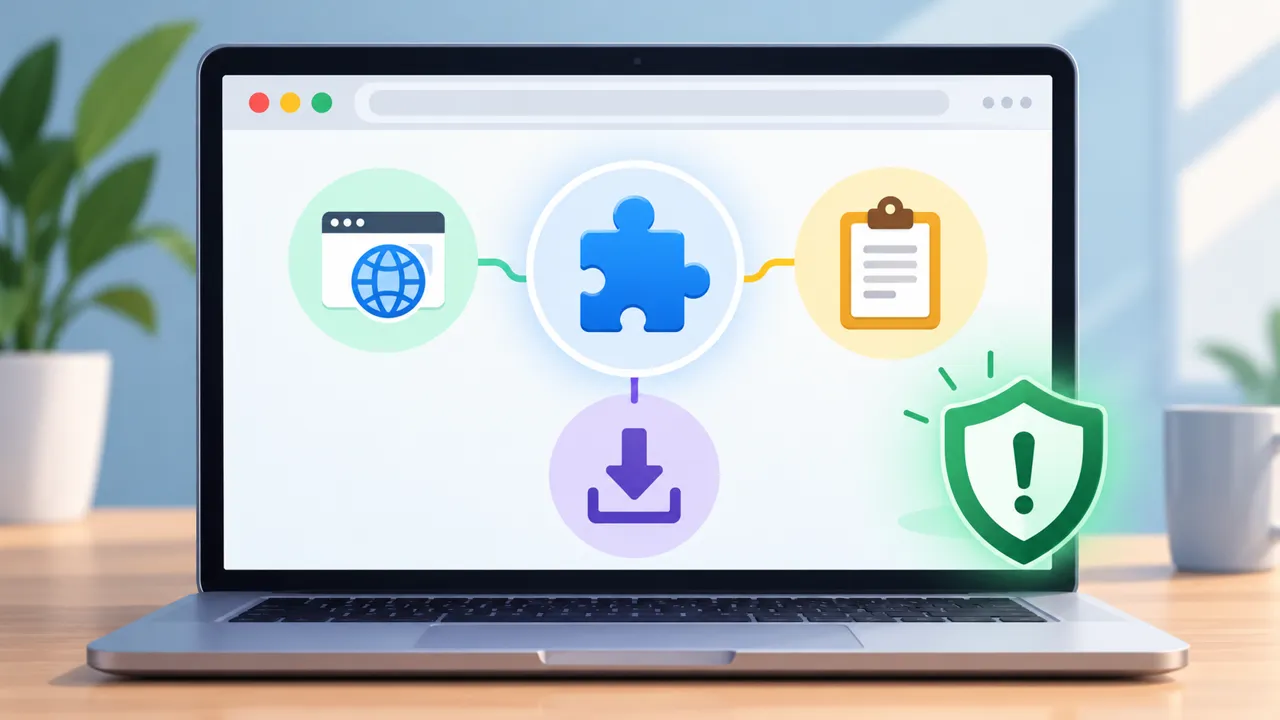
Review the publisher’s official site, privacy policy, support details, and recent updates. Watch for a sudden change in ownership or a major new permission request. A good history does not guarantee future safety, so keep the inventory current. If the extension cannot explain why it needs a new permission, pause the update or use until the team can review it.
Use trusted browser stores and company deployment methods where possible. Avoid installing unpacked or sideloaded extensions from links shared in chat unless a responsible developer has reviewed the source and business need. A store listing may offer useful signals, but it is not a substitute for your own risk review.
Set an Allowlist for Managed Devices
For a managed fleet, browser policies can limit what staff install. Microsoft Edge enterprise guidance describes ways to allow, block, and manage extensions through policy. Small teams may begin with a short approved list and a request process. Test the policy on a few devices before rolling it out widely.
Do not force-install every optional tool for everyone. Give staff only the extensions their role needs. An accounts worker and a designer may use different tools. A broad forced install can increase risk and create needless browser clutter.
Keep a way to request exceptions
Staff need a path to ask for new tools. A short request should explain the task, the desired extension, and the data it may see. Reviewers can check permissions and privacy terms, then approve a limited trial. Without a reasonable path, people may try to work around the policy.
Protect Passwords and Sessions
Extensions operate close to websites where people sign in. Keep multi-factor authentication on key accounts and use an approved password manager. Avoid putting passwords or session tokens into untrusted add-ons. If an extension is suspected of misuse, remove it from affected profiles, review account activity, and revoke sessions or tokens where needed.
Do not rely only on changing the browser password. A compromised session may remain active until it is revoked. Follow the account provider’s incident steps. Staff should report unusual prompts, surprise sign-outs, or unexpected changes to pages without fear of blame.
Review Privacy and Data Flow
Some extensions send page text or files to a cloud service to provide AI features. Ask what data leaves the browser, where it is stored, and how long it remains. Check whether it is used for model training and whether a company plan offers better controls. If the tool cannot meet the team’s data rules, do not use it on confidential pages.
For example, a grammar helper may need the words typed into a document. That can include private customer text or a draft contract. A safe decision may be to use the tool only on public marketing copy or choose a managed version with approved settings. Match the tool to the work rather than trying to make one extension acceptable everywhere.
Run a Short Practical Audit
Start with a pilot group of devices. Export or record the extension list, ask users which tools they need, and check each permission. Mark items as keep, restrict, review, or remove. Test that essential work still functions after a tool is disabled. Make changes in a way that staff can recover from if a workflow breaks.
A small team may find an old meeting capture add-on still active on every browser even though staff now use another tool. Removing it can reduce overlapping access and simplify support. Record the reason for the decision. Recheck the list after browser updates and staff changes.
What to do with an unknown extension
If the publisher or purpose is unclear, avoid using it for sensitive work while you investigate. Check the install source, permissions, and user. Remove it through the approved management process if it cannot be justified. If there is evidence of abuse, involve the security or IT contact and preserve relevant logs before making further changes.
Create a Review Schedule
Review high-permission extensions more often than simple tools. A quarterly check may be a sensible starting point for a small office, with extra review after new permissions, incidents, or ownership changes. Also remove access when an employee leaves or a project ends. An extension that had a good reason last year may have no reason today.
Keep the process short enough to repeat. One owner can maintain the list and ask department leads to confirm which tools are still needed. A useful record says what is approved, on which sites, for which roles, and when the decision expires.
A Browser Extension Security Checklist
- Inventory extensions by browser profile and user
- Remove unused or duplicate add-ons
- Review publisher and official privacy details
- Check permissions and sensitive site access
- Prefer approved stores and managed deployment
- Limit extensions by role
- Set a clear exception request path
- Review new permissions and ownership changes
- Plan session revocation for suspected misuse
- Recheck the list on a regular schedule
The checklist will not catch every malicious program. Endpoint protection, browser updates, account security, and staff training still matter. But extension control closes a gap that many teams overlook while focusing on larger software.
Common Mistakes
Do not approve a tool only because it has many downloads. Do not assume a browser store will review your private data needs. Do not leave a powerful extension installed because it once helped with a short project. And do not block every tool without explaining a useful alternative. A practical security process protects work while helping people keep doing it.
Final Takeaway
Browser extension security begins with knowing what is installed. Check access against the job, restrict sensitive sites, and keep an approved list that people can update. A short audit can reduce unseen data access without turning everyday browser work into a burden.
References
Chrome extension permission warnings and Microsoft Edge enterprise extension management.